❯
Hi, I'm Soumik.
Offensive security engineer and researcher working across web exploitation, malware analysis, and LLM defense. I test systems in controlled environments before adversaries find them in the wild, build tools to harden them, and actively pursue OSCP.

About
6+ years of hands-on offensive security experience, from responsible vulnerability disclosure and malware reverse engineering to darknet threat intelligence and building production-grade LLM security systems. Currently pursuing eJPT with OSCP as the next milestone, and ranked Top 2% globally on TryHackMe.
TryHackMe Field Activity
Daily engagement across offensive-security rooms throughout 2026.
160+ rooms completed · 150+ day streak · Top 2% global rank


Experience
Architected DataPlane, a production-grade LLM security engine sanitizing PII and prompt payloads before external model interaction. Led security and systems architecture and helped take the venture to VC discussions and investor pitches.
Architected DataPlane, a production-grade LLM security engine sanitizing PII and prompt payloads before external model interaction. Led security and systems architecture and helped take the venture to VC discussions and investor pitches.
Responsible disclosure across web and network infrastructure; malware reverse engineering; darknet OSINT and threat intelligence engagements.
Responsible disclosure across web and network infrastructure; malware reverse engineering; darknet OSINT and threat intelligence engagements.
Education
Certifications
Skills & Technologies
A structured overview of technical competencies spanning cybersecurity analysis, secure architecture, and modern software engineering.
Offensive Operations
Penetration Testing & Red Teaming
Forensics & Reverse Eng
Binary & Memory Analysis
Malware & Detection
Sandboxing & Detection Engineering
Crypto & Stego
Applied Cryptography & Steganography
Recon & Intel
OSINT & Attack Surface Intelligence
AI & LLM Systems
Agent Workflows & Model Security
Languages
Systems & Application Languages
Frontend
Modern Web Interfaces & Visualization
Backend & Data
Backend Architecture & Databases
DevOps & Tooling
CI/CD Automation & Infrastructure
Environments & Arenas
Virtual Labs & Attack Simulations
Projects
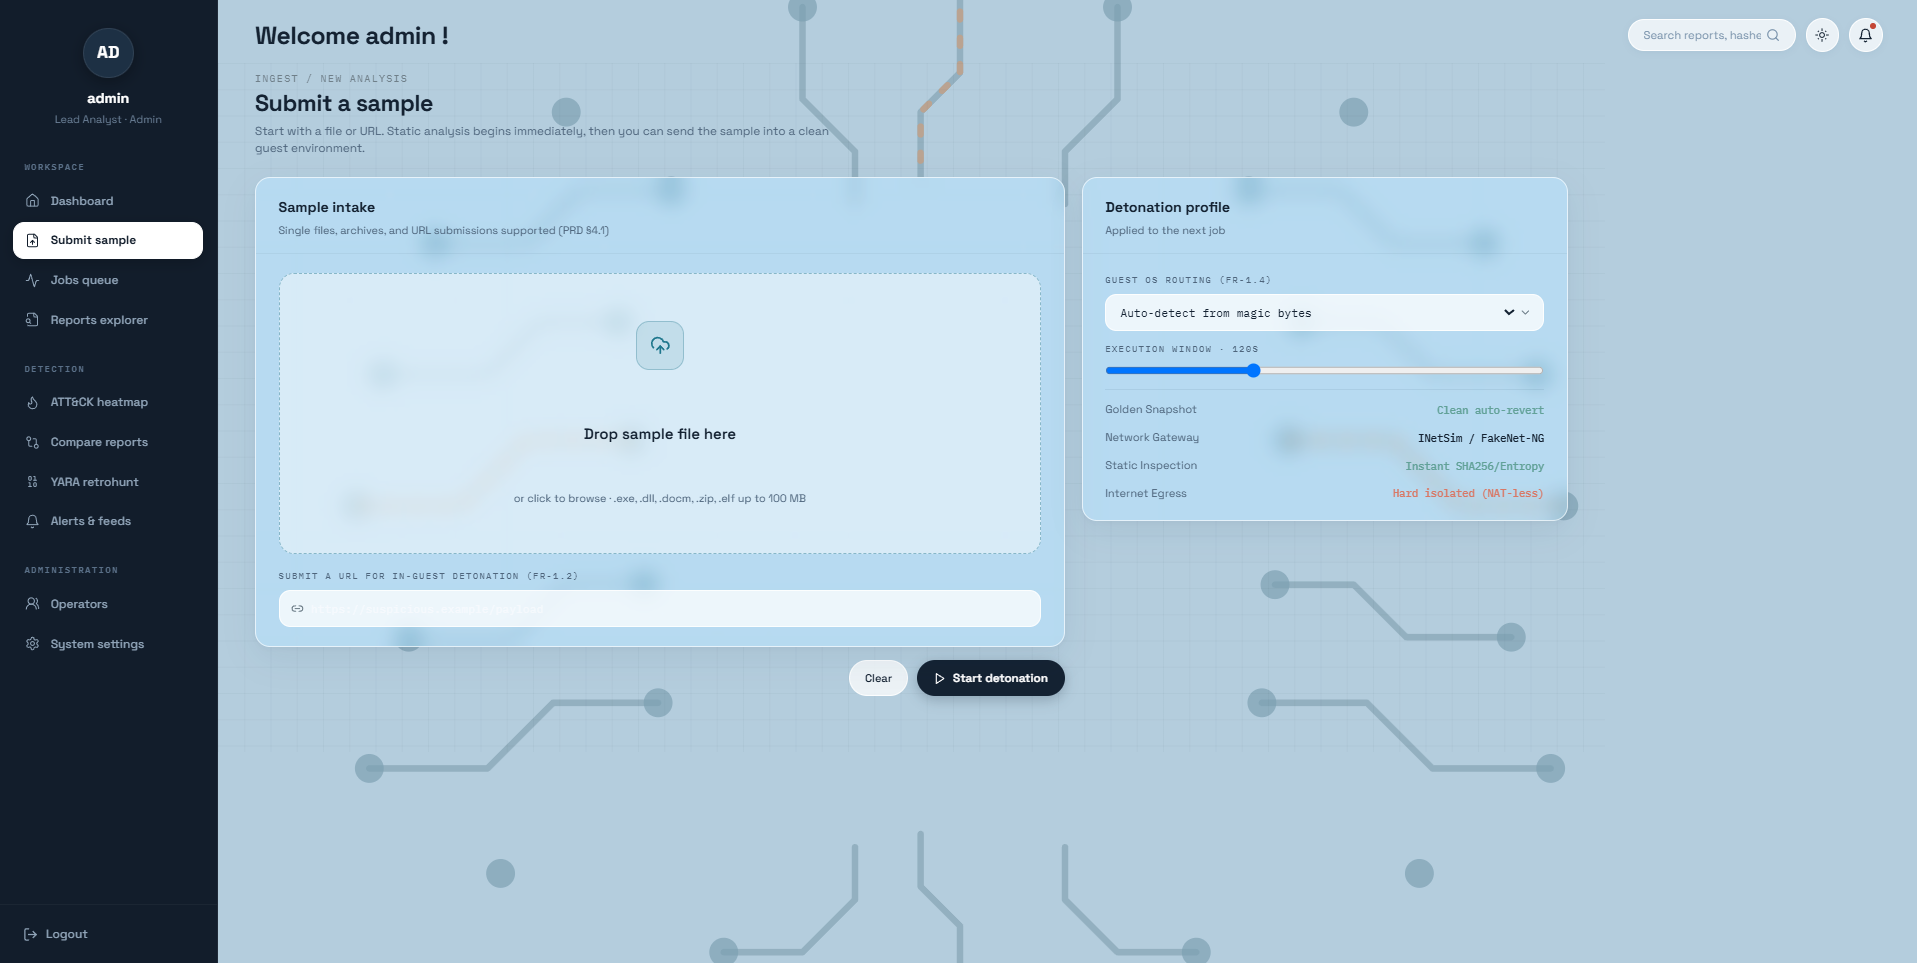
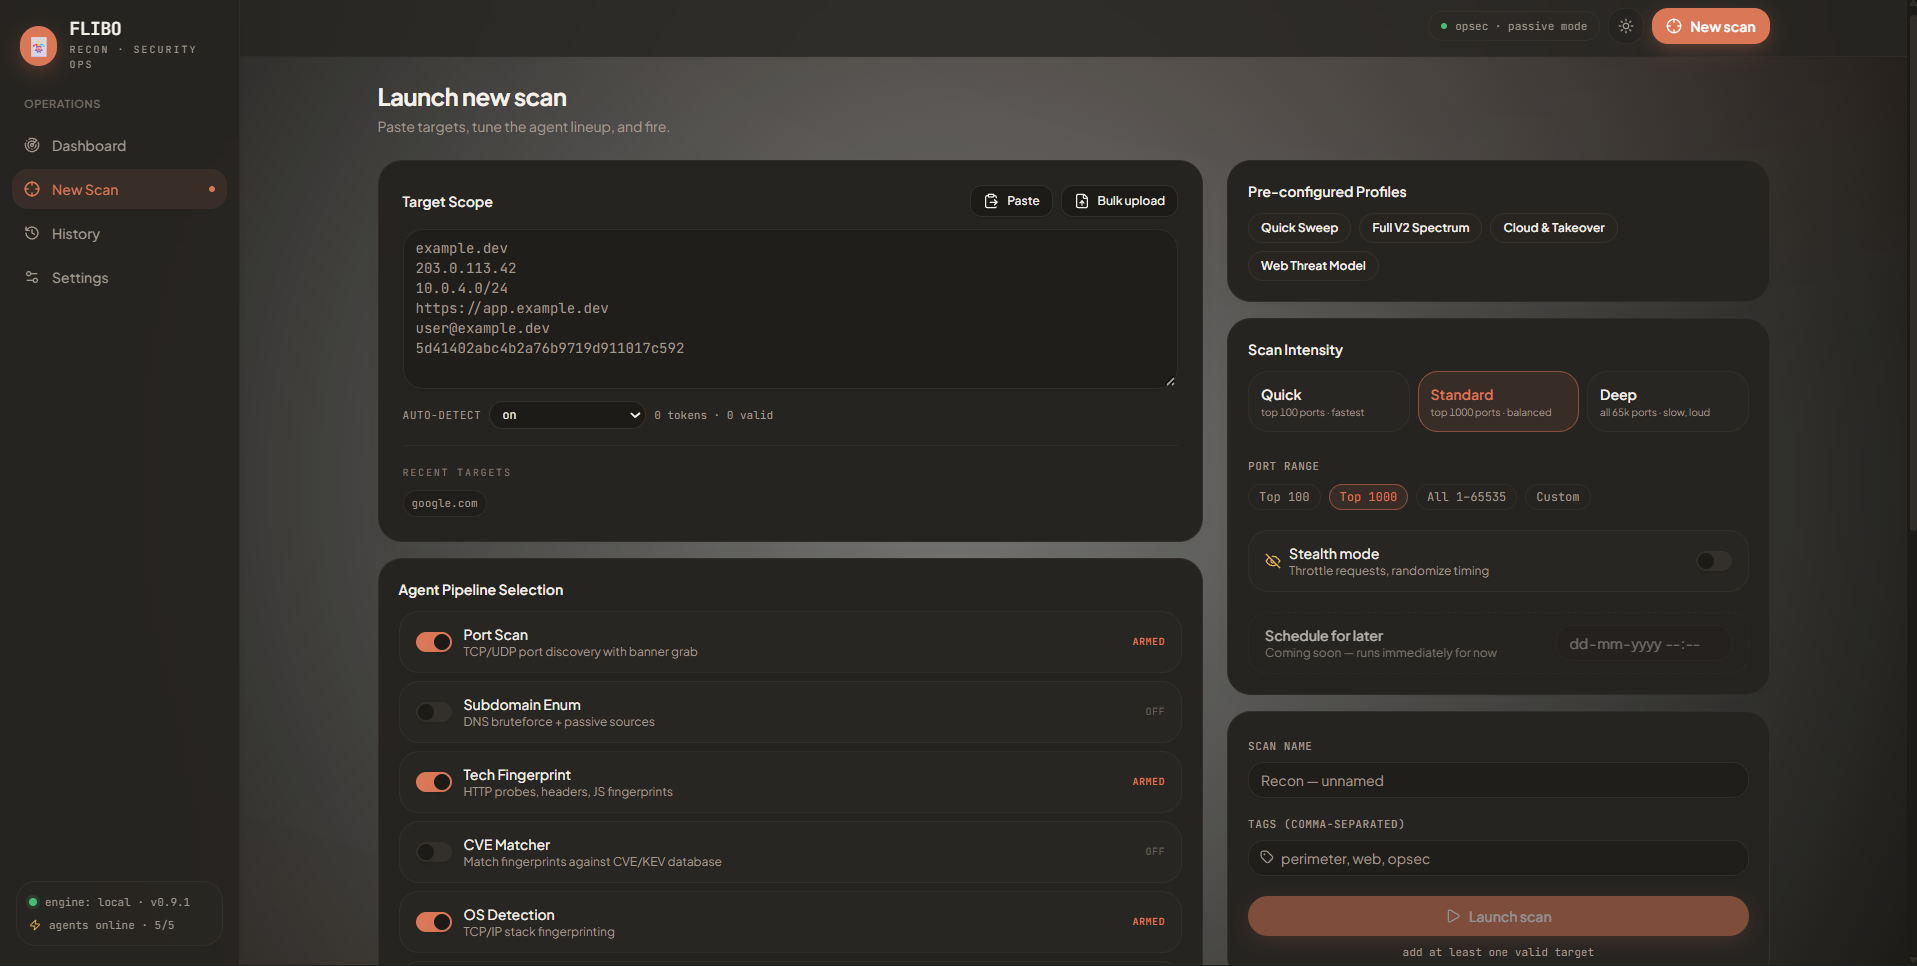
My projects and work across different technologies and domains.
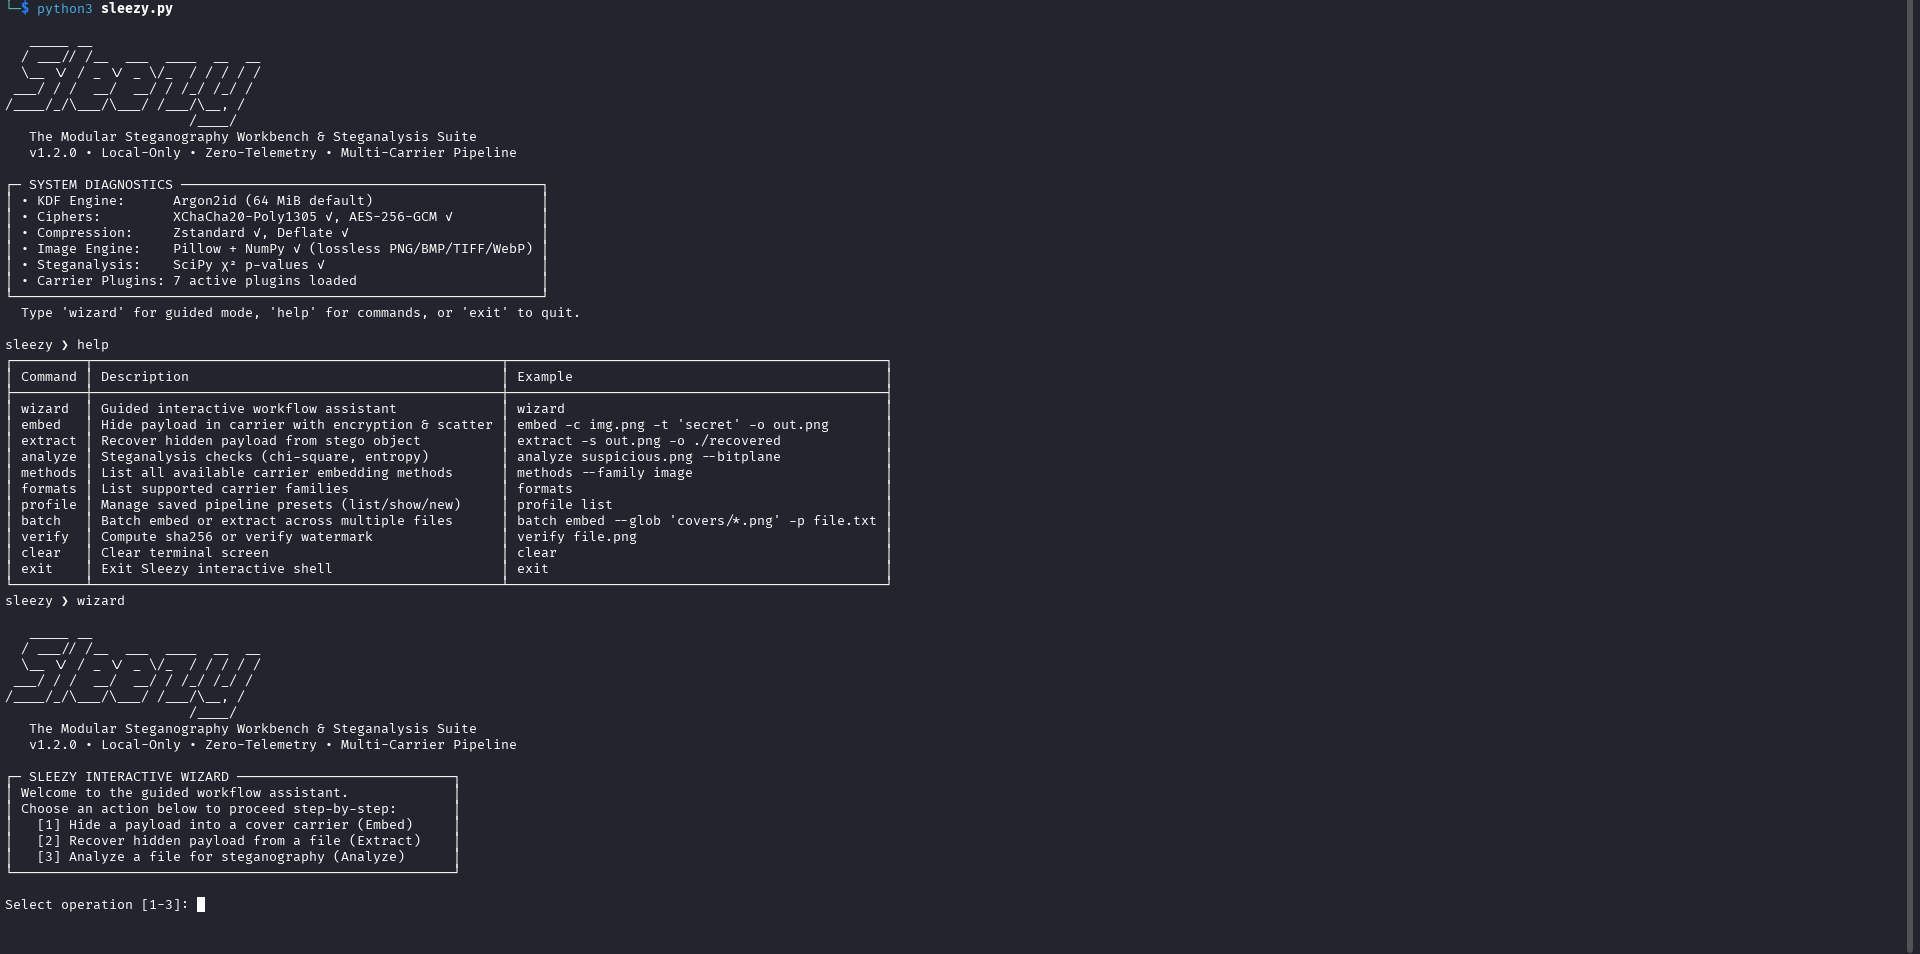
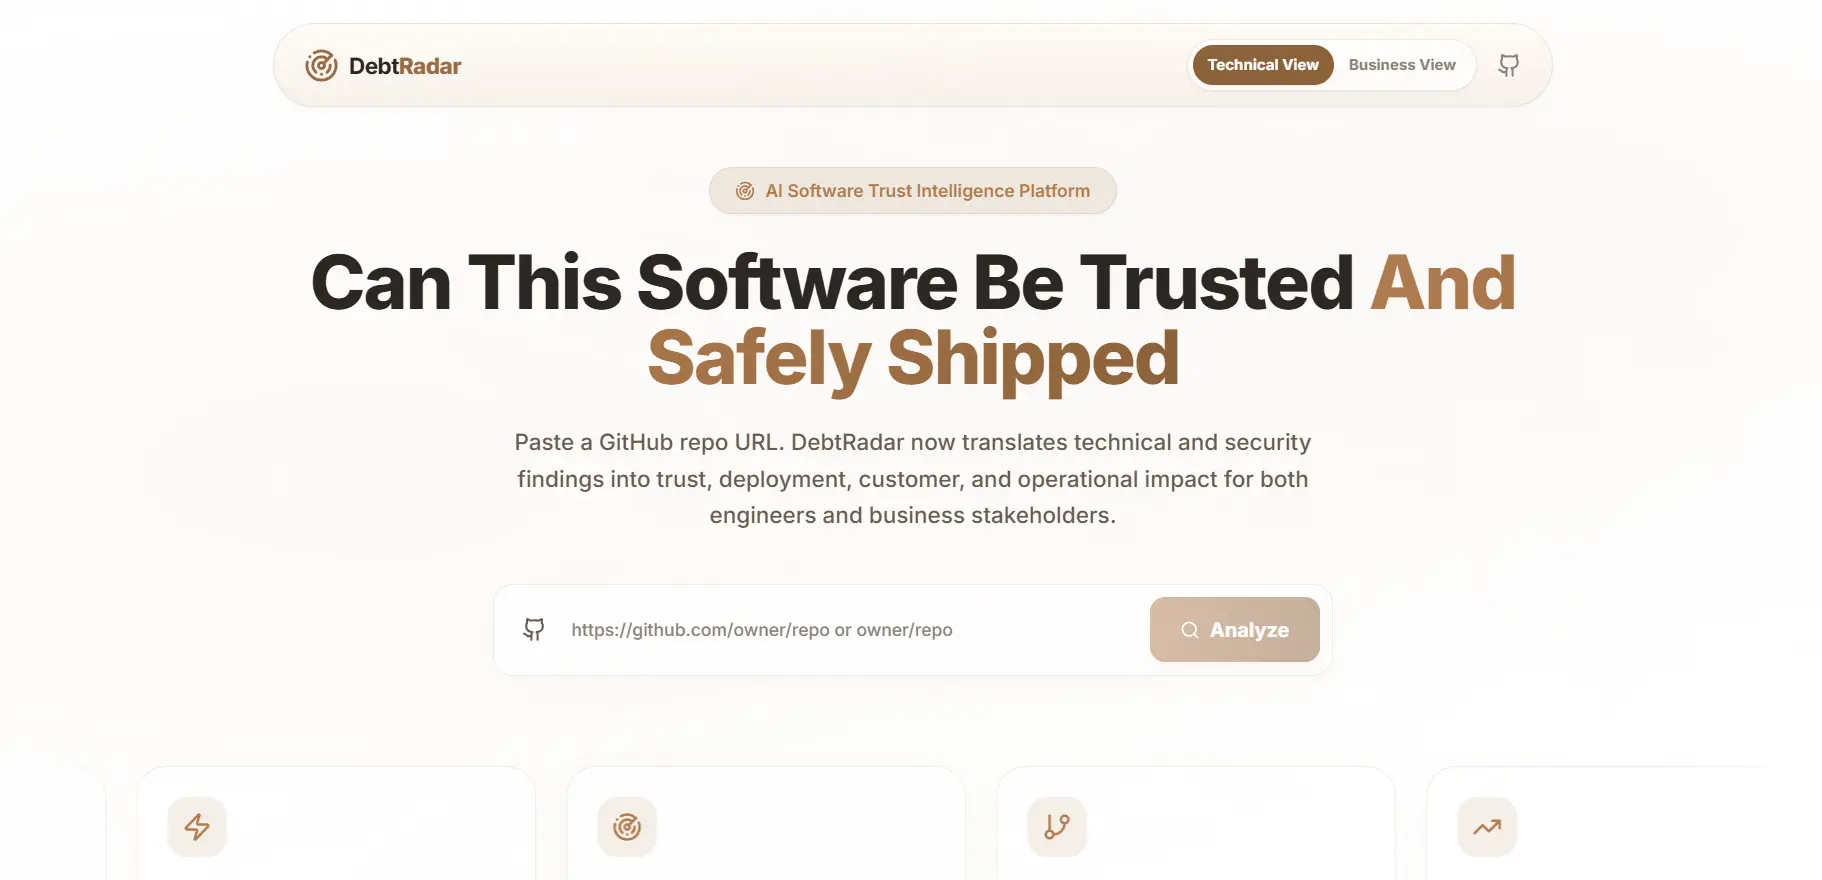
CTFs & Achievements
Navigating across offensive security milestones — from self-taught exploits and licensed pentesting to startup ventures and national finals.
Self-Taught Offensive Security
Started researching and exploiting independently, using SQLMap, Nmap, and SSH logins on live targets with no course and no guide. First SQL injection on a live site came out of three days of recon.
Licensed Penetration Tester
First official credential: a penetration tester license from Ficklem Pvt. Ltd, valid 2021 to 2026. Hobby turned into something with a name on it.
Malware, Tor, and Wargames
Kept widening the map. Malware analysis, Tor and darknet research, OverTheWire Bandit, and OWASP Juice Shop, learning from practical labs instead of slides.
Startup Ki Pathshala, Pitch Round
First competition after joining college. Pitched Sentinel AI, a secure AI shield layer, and got selected for the next round.
What The Hack, 1st Place
Won the first-ever GDG On Campus NSEC hackathon on our first attempt. Built a data privacy engine that strips PII before it reaches a model. It was built as a real product, not a one-off demo.
Co-Founder and CTO
The What The Hack project became a company. Co-founded FORETYX with my teammates and led security and system architecture, including DataPlane, the layer that sanitizes prompts before they reach an LLM. Helped take the venture to VC discussions and investor pitches.
HackArena 2.0, Regional Winners
Won the regional round and qualified for the national finals at IIIT Delhi.
Cisco NetAcad Stack
Worked through the Cisco certification ladder: Junior Analyst path, Ethical Hacker, Endpoint Security, Network Defense, and Cyber Threat Management.
TryHackMe, Top 2% Worldwide
Top 2% globally, Sapphire league, 150+ rooms, and a streak of 150+ days that's still going. Completed the Cyber Security 101 path.
SIH Internals, Top 10 of 230+
Team ZYRA topped the panel at the internal round with Argus, an AI system for criminal network analysis. The judges told us to patent it. Screening round is next.
Get in Touch
Open to junior pentest roles, security research collaborations, and freelance engagements. Reach out or drop an email; I read everything, I just don't do sales calls.
no phishing attempts please